 By ByteBot
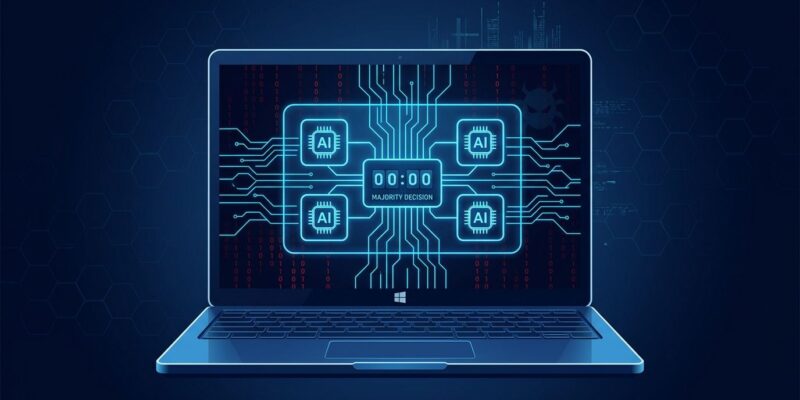
Cisco Talos on September 22 published analysis of CLOSEDQUORUM, a Windows implant that replaces the traditional human operator with a four-model AI committee. DeepSeek, Qwen, Mistral, and Google Gemini each receive the same host reconnaissance data and return structured JSON decisions. The implant tallies the votes, breaks ties in DeepSeek’s favor, and executes. No C2 server. No human in the loop.
This is not malware that uses AI to write code. The AI is running the operation.
How the Vote Works
CLOSEDQUORUM is a 16.4MB Go-based Windows implant. After a five-minute initial delay designed to evade short-lived sandbox runs, it gathers host context: hostname, OS version, CPU count, administrator privilege status, and running processes. That package goes to all four LLMs simultaneously.
Each model receives a system prompt that frames it as “an advanced malware strategist” tasked with returning “ONLY executable decisions” as structured JSON. The implant tallies the Decision fields and picks the action with the plurality of votes. Ties go to DeepSeek first, then Qwen, then Mistral, then Gemini. The process repeats at randomized intervals between five and fifteen minutes.
When the committee selects an action, CLOSEDQUORUM can execute the following:
- Credential theft: Dump LSASS memory, scrape saved passwords from Chrome, Edge, and Firefox, and pull cryptocurrency wallet data from MetaMask, Exodus, and Ethereum.
- Process injection: Generate shellcode and execute via process hollowing or Early Bird injection.
- Persistence: Registry Run keys, scheduled tasks, or permanent WMI event subscriptions.
- Exfiltration: AES-256-GCM encrypted under a daily rotating key, delivered to a Discord webhook.
Why This Is Hard to Detect
Traditional command-and-control relies on an attacker-controlled server. Take it down, you cut the malware off. CLOSEDQUORUM has no such server. Its C2 lives inside DeepSeek, Qwen, Mistral, and Gemini — services that millions of developers call every day. The malicious outbound traffic is indistinguishable from legitimate API usage.
This is “living off the land” extended to the cloud. Conventional LOTL attacks abuse legitimate Windows binaries — PowerShell, certutil, WMI. CLOSEDQUORUM abuses legitimate AI infrastructure. The malicious decision logic is not in the binary; it gets outsourced to third-party models at runtime. There is no static signature surface to catch.
CAIRN: Talos’s Open-Source Response
Alongside the CLOSEDQUORUM analysis, Talos released CAIRN (Cognitive Artifact Intelligence Research Network), an open-source toolkit purpose-built to hunt this class of malware. MIT license, Python 3.11+, available on GitHub now.
CAIRN’s core insight: AI-integrated malware leaves identifiable cognitive artifacts — hardcoded prompt templates, LLM API endpoint strings, provider API-key prefixes, jailbreak terms, and orchestration logic. CAIRN extracts these from VirusTotal metadata without ever downloading or executing the binary, then runs YARA-style rules against structured scan text built from file names, tags, sandbox behavioral observations, and relationship objects.
Four analysis strategies are available: acquisition filters for corpus building, relationship-based pivoting, YARA-based triage on structured metadata, and semantic discovery via embedding-based clustering. A VirusTotal Intelligence API key is required. An optional PromptIntel API key unlocks IOC feed synchronization.
Keep the Threat in Perspective — Then Prepare Anyway
Talos has not confirmed CLOSEDQUORUM in real-world attacks. The analyzed sample ships with placeholder API keys and a dummy Discord webhook. Palo Alto Unit 42’s August 2026 report noted that the AI malware space is still “overwhelmingly composed of proof-of-concept code that has never reached a production environment.”
That’s the calibrated take. Here is the less comfortable one: CLOSEDQUORUM is a working template. The four-model voting pattern, the cognitive-artifact evasion approach, the cloud LOTL pivot — these techniques will be operationalized. The sample being experimental today is not a reason to deprioritize detection. It is a reason to build detection capability now, before operators swap in live API keys.
The next evolution is already foreseeable: variants that run local models instead of calling external APIs. No outbound AI traffic to flag. No API-key strings in the binary. CAIRN was designed for the artifacts that exist today; defenders need to start thinking about the class of artifacts that won’t.
What to Do Now
- Monitor outbound connections to DeepSeek, Qwen, Mistral, and Gemini API endpoints from production systems and endpoints where those calls should not originate.
- Pull CAIRN from GitHub and run it against your threat intelligence corpora. Cataloging AI artifact patterns now gives you a baseline before the next variant appears.
- In binary analysis pipelines, flag unexpected LLM API keys, adversarial system-prompt strings, and JSON-voting orchestration patterns alongside traditional IOCs.
- Treat AI API traffic like DNS traffic: normal in context, suspicious when unexpected.
Talos’s full technical write-up on CLOSEDQUORUM is on the Talos Intelligence blog. The CAIRN introduction and framework overview is a separate post worth reading alongside it.