 By ByteBot
A zero-click remote code execution flaw hit all four major AI coding agents at once — Claude Code, OpenAI Codex, GitHub Copilot, and Google Gemini CLI. Before researchers could pull a proof-of-concept, it had already spread to 26,000 agents. The vulnerability is called Plugin4Shell, and the reason it worked is more unsettling than the name: the safety mechanism everyone assumed was working wasn’t.
The Flaw That Fooled Four Teams
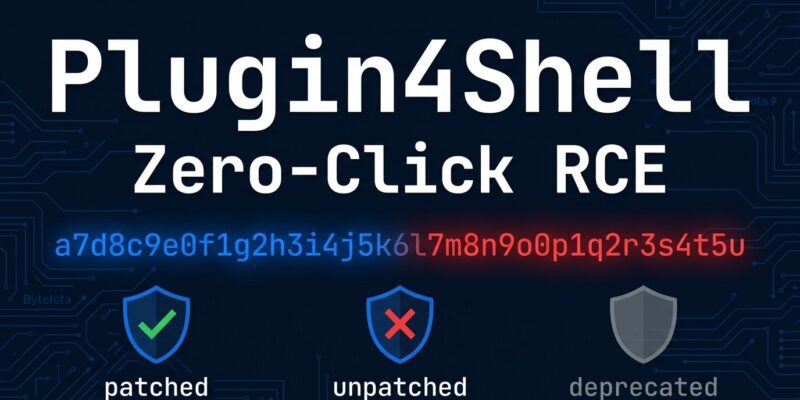
Every major coding agent uses SHA pinning to lock plugins to a specific, reviewed commit. The idea is sound — pin to a 40-character commit hash, and users run exactly what was audited. But there is a gap between specifying a SHA and verifying it.
Git’s reference resolution has a priority order. When an agent calls git checkout <sha>, git checks branch names before commits. An attacker who controls a plugin’s repository can create a branch whose name is that exact 40-character SHA. Git resolves to the branch — attacker-controlled — instead of the commit. The agent proceeds as though the pinned, reviewed code loaded. It didn’t.
What makes this a systemic failure rather than a single team’s mistake: all four agent codebases were written independently and all four made the same wrong assumption. The fix — read back the actual HEAD after checkout and compare it to the pinned SHA, abort if they differ — is a two-line addition. Nobody added those two lines.
Who Is Patched, Who Isn’t
AIR Security researchers Or Nevo, Dor Granat, and Niv Hoffman reported Plugin4Shell to all four vendors in June 2026, then published full disclosure on September 17. Here is where each agent stands:
- Claude Code: Patched. Anthropic shipped the fix in version 2.1.179 — in June, three months before public disclosure. Running 2.1.179 or later means you are safe.
- OpenAI Codex: Patched. Fixed in version 0.146.0, shipped around September 10.
- GitHub Copilot: Unpatched as of September 21. Microsoft received the disclosure in June and has not shipped a fix or published a CVE. There is no official timeline.
- Gemini CLI: Won’t be patched. Google retired Gemini CLI on June 18, 2026 — replaced by Antigravity CLI — and told AIR Security it will not issue a fix for the deprecated tool. Every remaining Gemini CLI install is permanently exposed.
Why This Was Zero-Click
Claude Code and Codex update installed plugins automatically in the background by default. When a marketplace bumps a pinned SHA, the update reaches already-installed plugins without any user prompt, approval, or reinstall. The victim only needs to have a plugin installed from a trusted marketplace — that is the entire attack surface.
An AI coding agent running on a developer’s machine has full filesystem access, reads environment variables, can spawn processes, and has network access. A successful Plugin4Shell exploit gives an attacker everything the agent can touch — which in most developer environments means source code, API keys, and cloud credentials.
The Bigger Problem Behind the Flaw
Plugin4Shell is the clearest illustration yet of a risk building quietly: AI coding agent plugin marketplaces have grown rapidly without the security infrastructure to make them safe to trust. The AIR Security proof-of-concept spreading to 26,000 agents before detection is not just a statistic — it is a demonstration of how quickly a trusted distribution channel becomes an attack surface when the verification layer is missing.
This is the npm supply chain problem reprised in a context where the stakes are higher. Packages can exfiltrate data; a compromised coding agent plugin can do that and more, with an LLM to help cover its tracks. The Cloud Security Alliance flagged AI agent supply chain risk earlier this year — Plugin4Shell is the first major public exploit to make that warning concrete.
What to Do Right Now
Check your version. The update is the entire fix for Claude Code and Codex users.
- Claude Code: Run
claude --version. If below 2.1.179, update:npm update -g @anthropic-ai/claude-code - Codex: Verify you are on 0.146.0 or later.
- GitHub Copilot: No patch exists yet. Audit installed plugins, disable any connecting to external repositories, and consider turning off auto-updates until Microsoft ships a fix. Monitor the ongoing coverage at The Register for patch updates.
- Gemini CLI: Migrate to Antigravity CLI. A patch is not coming.
The deeper lesson is one the industry will keep relearning: pinning to a hash is not the same as verifying a hash. In a world where coding agents run with the access level of a logged-in developer, that distinction cannot be an afterthought.