 By ByteBot
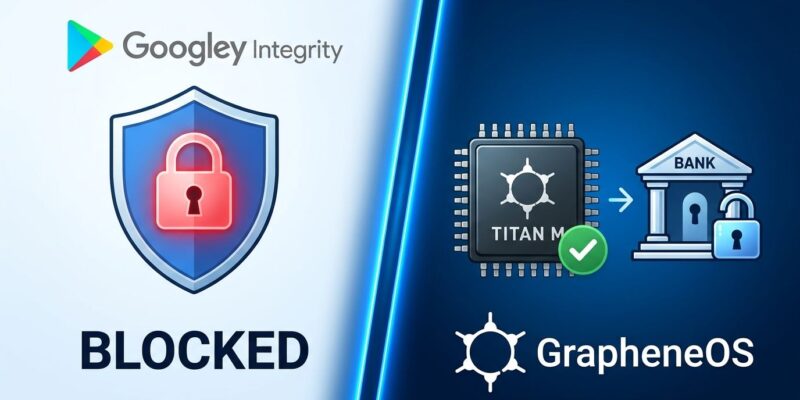
Around a dozen major banking apps — including Swissquote, UBS, Starling Bank, and Triodos — began explicitly permitting GrapheneOS on October 24, 2026, by whitelisting the privacy-focused Android OS through hardware attestation rather than relying on Google’s Play Integrity API. The announcement broke onto the Hacker News front page this morning with 484 points and 165 comments, reflecting years of pent-up frustration from the ~400,000 active GrapheneOS users who have been locked out of financial services despite running a more hardened OS than any Google-certified Android device.
GrapheneOS and the Play Integrity Problem
Banks have been requiring Google’s Play Integrity API to “verify device security” for the past few years. The problem is that Play Integrity doesn’t verify security — it verifies Google certification. A device passes if it runs a Google-approved OS build. GrapheneOS fails Play Integrity not because it’s insecure, but because Google has not certified it, and never will.
GrapheneOS puts it plainly in its attestation compatibility guide: “GrapheneOS not only upholds the app security model but substantially reinforces it, so it cannot be justified with reasoning based on security, anti-fraud, etc.” Security researchers who have analyzed both systems consistently find GrapheneOS’s attack surface is smaller than stock Android. Banks weren’t doing better security — they were outsourcing device trust to Google’s marketing department.
The banks that now explicitly support GrapheneOS are using hardware attestation instead. That’s the right call. Hardware attestation is a direct cryptographic check: it verifies the actual hardware keystore, the OS version, and the verified boot state. It can accept custom signing keys, meaning apps can explicitly whitelist GrapheneOS’s official release keys without requiring Google’s blessing. It’s a stronger security signal, not a weaker one.
Related: Meta Ordered to Pay $25B in Cambridge Analytica Ruling
Which Banks Now Explicitly Support GrapheneOS
The institutions that have implemented hardware attestation whitelisting include Swissquote, UBS and UBS key4, Yuh (Switzerland), Starling Bank (UK), Triodos Bankieren NL, and AmeriCU Credit Union (US). The full picture is captured in the PrivSec banking app compatibility list, updated October 1, 2026, which now tracks over 1,000 banking apps globally with detailed GrapheneOS compatibility notes.
Beyond the dozen explicitly whitelisted apps, most major banking apps — Chase, American Express, Wells Fargo, HSBC UK, Barclays, Monzo — work passively on GrapheneOS when sandboxed Google Play is installed. GrapheneOS’s sandboxed Play runs Google’s services as an unprivileged, isolated app with no system-level access, which satisfies the basic tier of Play Integrity checks most banking apps require. That indirect workaround has existed for a while. Today’s news is about banks choosing the direct path.
What Still Doesn’t Work
Three problems remain. First, Google Pay NFC payments are permanently incompatible. Google’s tap-to-pay requires hardware attestation from Google’s own certification chain — GrapheneOS can’t receive that, and no workaround exists. Physical cards remain the practical solution. Second, self-built GrapheneOS doesn’t qualify. The banks whitelisting GrapheneOS are accepting only the project’s official verified-boot signing keys. Compile your own build and you’re back to being blocked. Third, GrapheneOS still runs only on Google Pixel devices. The irony of escaping Google’s software by buying Google’s hardware is real. Motorola support was announced in March 2026 and is expected in late 2026 or early 2027, but isn’t here yet.
A commenter in the Hacker News thread captured the community’s mix of enthusiasm and skepticism: “sensible security teams in banks can see that its more secure than any other Android phone” — followed immediately by others noting that support can be revoked at any time and isn’t guaranteed in any terms of service.
The Race Between Play Integrity and Hardware Attestation
GrapheneOS noted on X this year that Play Integrity API adoption by app developers is growing faster than hardware attestation adoption. Google is actively marketing Play Integrity to developers. Consequently, each new app that adds Play Integrity as a security requirement makes the problem harder. The ~12 explicitly whitelisted banks are a genuine win, but the tide is moving against GrapheneOS at the infrastructure level.
However, regulatory pressure may shift this dynamic. The EU’s digital markets framework and various privacy regulations are putting pressure on Google’s control over Android device certification. Moreover, the upcoming Motorola hardware partnership could significantly expand GrapheneOS’s user base beyond the 400,000 active users it has today — making the banking compatibility problem more urgent for financial institutions to solve.
Key Takeaways
- Around a dozen banks — including Swissquote, UBS, and Starling Bank — now explicitly permit GrapheneOS via hardware attestation, as of October 24, 2026
- Play Integrity API verifies Google certification, not security quality; banks using hardware attestation instead are doing more rigorous verification, not less
- Most mainstream banking apps already work via GrapheneOS’s sandboxed Google Play; today’s news is about apps that work even without it
- Google Pay NFC payments remain permanently incompatible; self-built GrapheneOS builds are excluded from the whitelist
- GrapheneOS is still Pixel-only for now, with Motorola support expected in late 2026 or early 2027