 By ByteBot
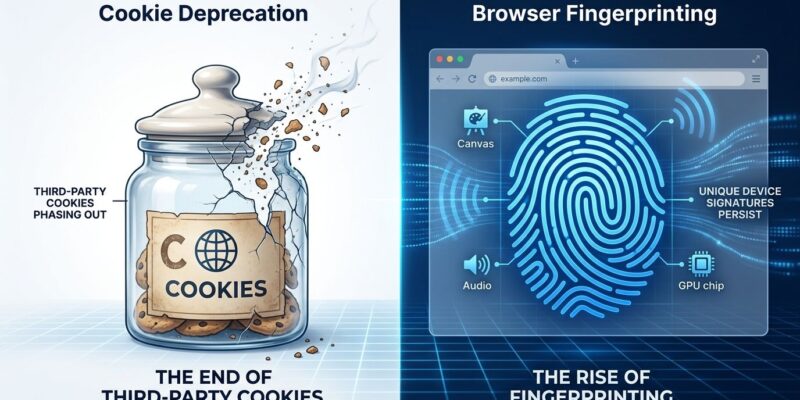
Google spent six years telling the world it was killing third-party cookies to protect your privacy. Then it shipped browser fingerprinting instead — a tracking method that cannot be blocked, cannot be deleted, and now runs on 78% of the top 10,000 websites according to the EFF’s 2026 fingerprinting survey. That number was 61% two years ago. The industry didn’t find a privacy-friendly alternative to cookies. It found a worse one.
What Browser Fingerprinting Is — And Why “Clear Data” Doesn’t Touch It
Cookies store tracking data on your device. You can delete them. Browser fingerprinting reads your device’s technical characteristics — GPU model, CPU audio processing behavior, font rendering quirks, timezone — and builds a persistent identifier from the results. Nothing is written to your machine, so there is nothing to erase.
Six browser APIs do the heavy lifting, and most of them are ones you’ve probably used in legitimate code: OfflineAudioContext, WebGL, Canvas, the Intl API, navigator, and crypto.subtle. The audio context fingerprint is the sneakiest. It exploits floating-point differences in how your CPU processes a signal through an audio compressor. No sound plays. No permission prompt appears.
const ctx = new OfflineAudioContext(1, 44100, 44100);
const oscillator = ctx.createOscillator();
const compressor = ctx.createDynamicsCompressor();
oscillator.connect(compressor);
compressor.connect(ctx.destination);
oscillator.start(0);
ctx.startRendering().then(buffer => {
  const fingerprint = buffer.getChannelData(0).slice(4500, 4600);
  // CPU-specific floating-point differences create a unique, persistent signature
});
Stack Canvas (roughly 16 bits of entropy), WebGL (roughly 14 bits), and AudioContext (roughly 11–12 bits) together and you can uniquely identify approximately 1 in 250,000 users before pulling any other signals. That fingerprint survives cookie clearing, private browsing, and most VPN setups. VPNs mask your IP address. However, they do nothing about your GPU vendor, your CPU’s audio processing quirks, or the timezone your Intl API reports — which is read directly from your OS, not your network.
Google Killed Cookies. Then It Enabled Fingerprinting.
The timeline matters here. In 2019, Google announced it would phase out third-party cookies by 2022 and replace them with Privacy Sandbox — a set of on-device APIs designed to enable advertising without exposing individual identifiers. By April 2025, Google had killed Privacy Sandbox entirely. Six years of delays, and the UK Competition and Markets Authority’s testing had been brutal: 85% attribution inaccuracy and a 30% drop in publisher revenue. Zero fingerprinting mitigations were ever shipped.
Also in 2025, Google reversed its stated position on fingerprinting — from “digital fingerprinting is wrong” to “it’s acceptable if disclosed” — and enabled it in its advertising products. The UK Information Commissioner’s Office called the move “irresponsible.” Privacy consultant Alexander Hanff documented the result in The Register’s April 2026 report: “There are at least thirty distinct fingerprinting techniques that work in Chrome right now, today. Chrome ships almost no built-in anti-fingerprinting defenses.”
Safari blocks third-party cookies by default. Firefox blocks them. Brave blocks them. Chrome still allows them — and now fingerprinting too. The company that spent six years promising to fix the privacy problem instead ratified the replacement. We covered a similar pattern with Passkeys Are a Trap, where a “privacy-improving” standard turned out to carry its own hidden surveillance layer.
The 78% Stat Is a Chrome Problem
The EFF’s jump from 61% to 78% fingerprinting adoption didn’t happen randomly. Trackers migrated to the method the dominant browser doesn’t defend against. EFF researcher Dr. Hesper Caraballo-Wright was direct: “The reason fingerprinting is at 78 percent is not that the countermeasures do not exist. It is that the dominant browser has not shipped them meaningfully.”
The countermeasures exist. Firefox ships privacy.resistFingerprinting. Brave injects per-session noise into canvas and audio outputs — a technique called “farbling” — making consistent cross-session profiling significantly harder. Mullvad Browser takes the opposite approach: rather than randomizing, it makes all users present identical fingerprints, so individual identification becomes statistically impossible. Tor Browser does the same, with onion routing on top.
Chrome has none of this. Moreover, after Manifest V3, full uBlock Origin no longer runs on Chrome. Users are left with uBlock Origin Lite, which the developer has stated cannot prevent API-level fingerprinting. ByteIota previously reported on how this same pattern shows up with Cloudflare Turnstile’s WebGL fingerprinting — specific services fingerprinting users through APIs that Chrome provides without restriction.
What Developers Should Actually Do
If you’re building web applications, assume your third-party analytics SDKs, ad scripts, and CDN-loaded libraries are fingerprinting your users — whether you asked them to or not. The State of Browser Privacy 2026 guide recommends server-side analytics over client-side tracking scripts, IP truncation before storage, and quarterly audits of every third-party script your application loads. CSP headers that block unauthorized script sources are not optional if you’re claiming to protect user privacy.
For your own browser, the analysis trending on Hacker News this week found only three browsers provide meaningful fingerprint resistance — Brave, Tor, and Mullvad. Privacy extensions make things worse, not better: a rare extension is itself a highly unique signal that increases your entropy. Cookie clearers solve a problem that stopped being the main problem when Google decided fingerprinting was acceptable after all.